Our systems detected an issue with your IP. If you think this is an error please submit your concerns via our contact form.
Identify and Manage Regulatory and Compliance Risk Impacts on Your Organization
It is easier for prospective clients to find out what you did wrong than that you fixed the issue.
More than at any other time, our world is changing. As a result, organizations – and their vendors – need to be able to adapt their plans to accommodate risk on an unprecedented level.
It is increasingly likely that one of your vendors, or their n-party support vendors, will fall out of regulatory compliance. Therefore, organizations must protect themselves by creating better mechanisms to hold their n-party vendors accountable and validate that they comply.

Our Advice
Critical Insight
- Identifying and managing a vendor’s potential regulatory impact on your organization requires multiple people in the organization across several functions. Those people all need coaching on the potential changes in the market and how these changes may affect operations.
- Organizational leadership is often taken unaware by changes, and their plans lack the flexibility to adjust to significant regulatory upheavals.
Impact and Result
Vendor management practices educate organizations on the different potential risks from vendors in your market and suggest creative and alternative ways to avoid and help manage them.
- Prioritize and classify your vendors with quantifiable, standardized rankings.
- Prioritize focus on your high-risk vendors.
- Standardize your processes for identifying and monitoring vendor risks with our Regulatory Risk Impact Tool to manage potential impacts.
Research & Tools
1. Identify and Manage Regulatory and Compliance Risk Impacts to Your Organization Storyboard – Use the research to better understand the negative impacts of vendor actions to your brand reputation.
Use this research to identify and quantify the potential regulatory impacts caused by vendors. Use Info-Tech's approach to look at the regulatory impact from various perspectives to better prepare for issues that may arise.
2. Regulatory Risk Impact Tool – Use this tool to help identify and quantify the operational impacts of negative vendor actions.
By playing the “what if” game and asking probing questions to draw out – or eliminate – possible negative outcomes, everyone involved adds their insight into parts of the organization to gather a comprehensive picture of potential impacts.
Identify and Manage Risk Impacts on Your Organization
It is easier for prospective clients to find out what you did wrong than that you fixed the issue.
Analyst perspective
Organizations must understand the regulatory damage vendors may cause from lack of compliance.
 |
The sheer number of regulations on the international market is immense, ever-changing, and make it almost impossible for any organization to consistently keep up with compliance. As regulatory enforcement increases, organizations must hold their vendors accountable for compliance through ongoing monitoring and validation of regulatory compliance to the relevant standards in their industries, or face increasing penalties for non-compliance. Frank Sewell, Research Director, Vendor Management Info-Tech Research Group |
Executive Summary
Your Challenge |
Common Obstacles |
Info-Tech’s Approach |
|---|---|---|
More than at any previous time, our world is changing rapidly. As a result, organizations – and their vendors – need to be able to adapt their plans to accommodate risk on an unprecedented level. It is increasingly likely that one of your vendors, or their n-party support vendors, will fall out of regulatory compliance. Organizations must protect themselves by creating better mechanisms to hold their n-party vendors accountable and validate that they comply. |
Identifying and managing a vendor’s potential regulatory impact on your organization requires multiple people in the organization across several functions. Those people all need coaching on the potential changes in the market and how these changes may affect operations. Organizational leadership is often taken unaware by changes, and their plans lack the flexibility to adjust to significant regulatory upheavals. |
Vendor management practices educate organizations on the different potential risks from vendors in your market and suggest creative and alternative ways to avoid and help manage them. Prioritize and classify your vendors with quantifiable, standardized rankings. Prioritize focus on your high-risk vendors. Standardize your processes for identifying and monitoring vendor risks with our Regulatory Risk Impact Tool to manage potential impacts. |
Info-Tech Insight
Organizations must evolve their risk assessments to be more adaptive to respond to regulatory changes in the global market. Ongoing monitoring of the vendors who must comply with industry and governmental regulations is crucial to avoiding penalties and maintaining your regulatory compliance.
Info-Tech’s multi-blueprint series on vendor risk assessment
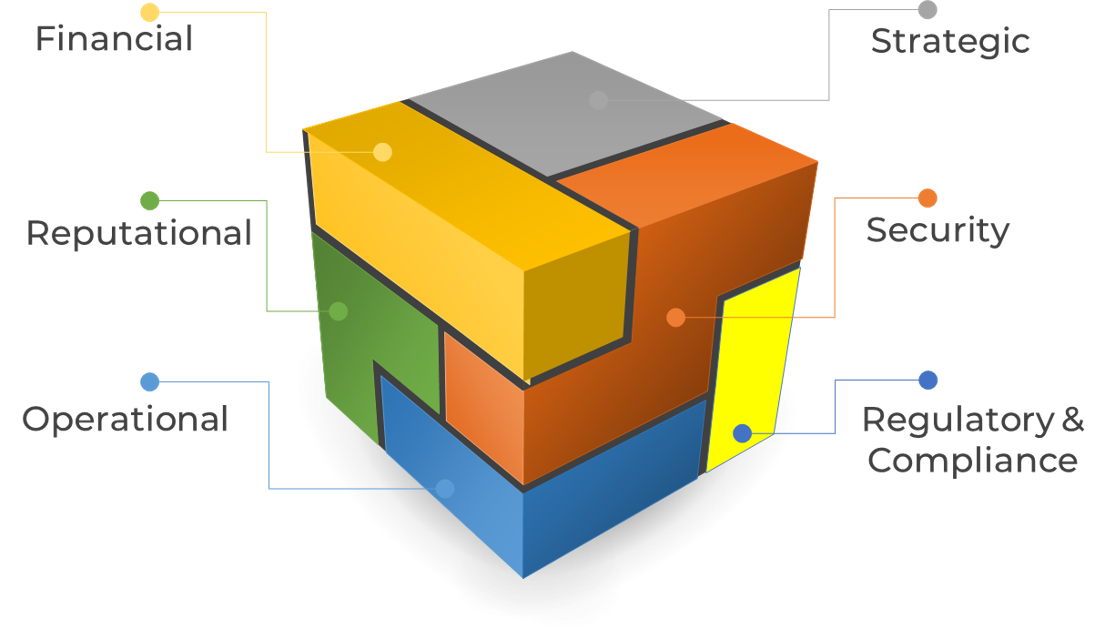
There are many individual components of vendor risk beyond cybersecurity.

This series will focus on the individual components of vendor risk and how vendor management practices can facilitate organizations’ understanding of those risks.
Out of Scope:
This series will not tackle risk governance, determining overall risk tolerance and appetite, or quantifying inherent risk.
Regulatory and Compliance risk impacts
Potential losses to the organization due regulatory and compliance incidents.
- In this blueprint we’ll:
- Explore regulatory and compliance risks and their impacts.
- Identify potentially disruptive events to assess the overall impact on organizations and implement adaptive measures to identify, manage, and monitor vendor performance.
This content is exclusive to members.
Sign up to continue reading the full blueprint, or sign in if you already have an account.
Our systems detected an issue with your IP. If you think this is an error please submit your concerns via our contact form.