Develop and Implement a Security Incident Management Program
Create a scalable incident response program without breaking the bank.
Security incidents are inevitable, but how they’re dealt with can make or break an organization. Poor incident response negatively affects business practices, including workflow, revenue generation, and public image.
The incident response of most organizations is ad hoc at best. A formal management plan is rarely developed or adhered to, resulting in ineffective firefighting responses and inefficient allocation of resources.
Our Advice
Critical Insight
Embrace the use of ready-made responses when handling incidents. These pre-established response plans can save valuable time and effort during a crisis. By relying on proven and tested procedures, your team can respond swiftly and efficiently, minimizing the impact of incidents and ensuring a consistent approach to resolving security breaches.
Analyze, track, and review results of incident response regularly. Without a comprehensive understanding of incident trends and patterns, you can be revictimized by the same attack vector.
Establish communication processes and channels well in advance of a crisis. Don’t wait until a state of panic. Collaborate and exchange information with other organizations to stay ahead of incoming threats.
Impact and Result
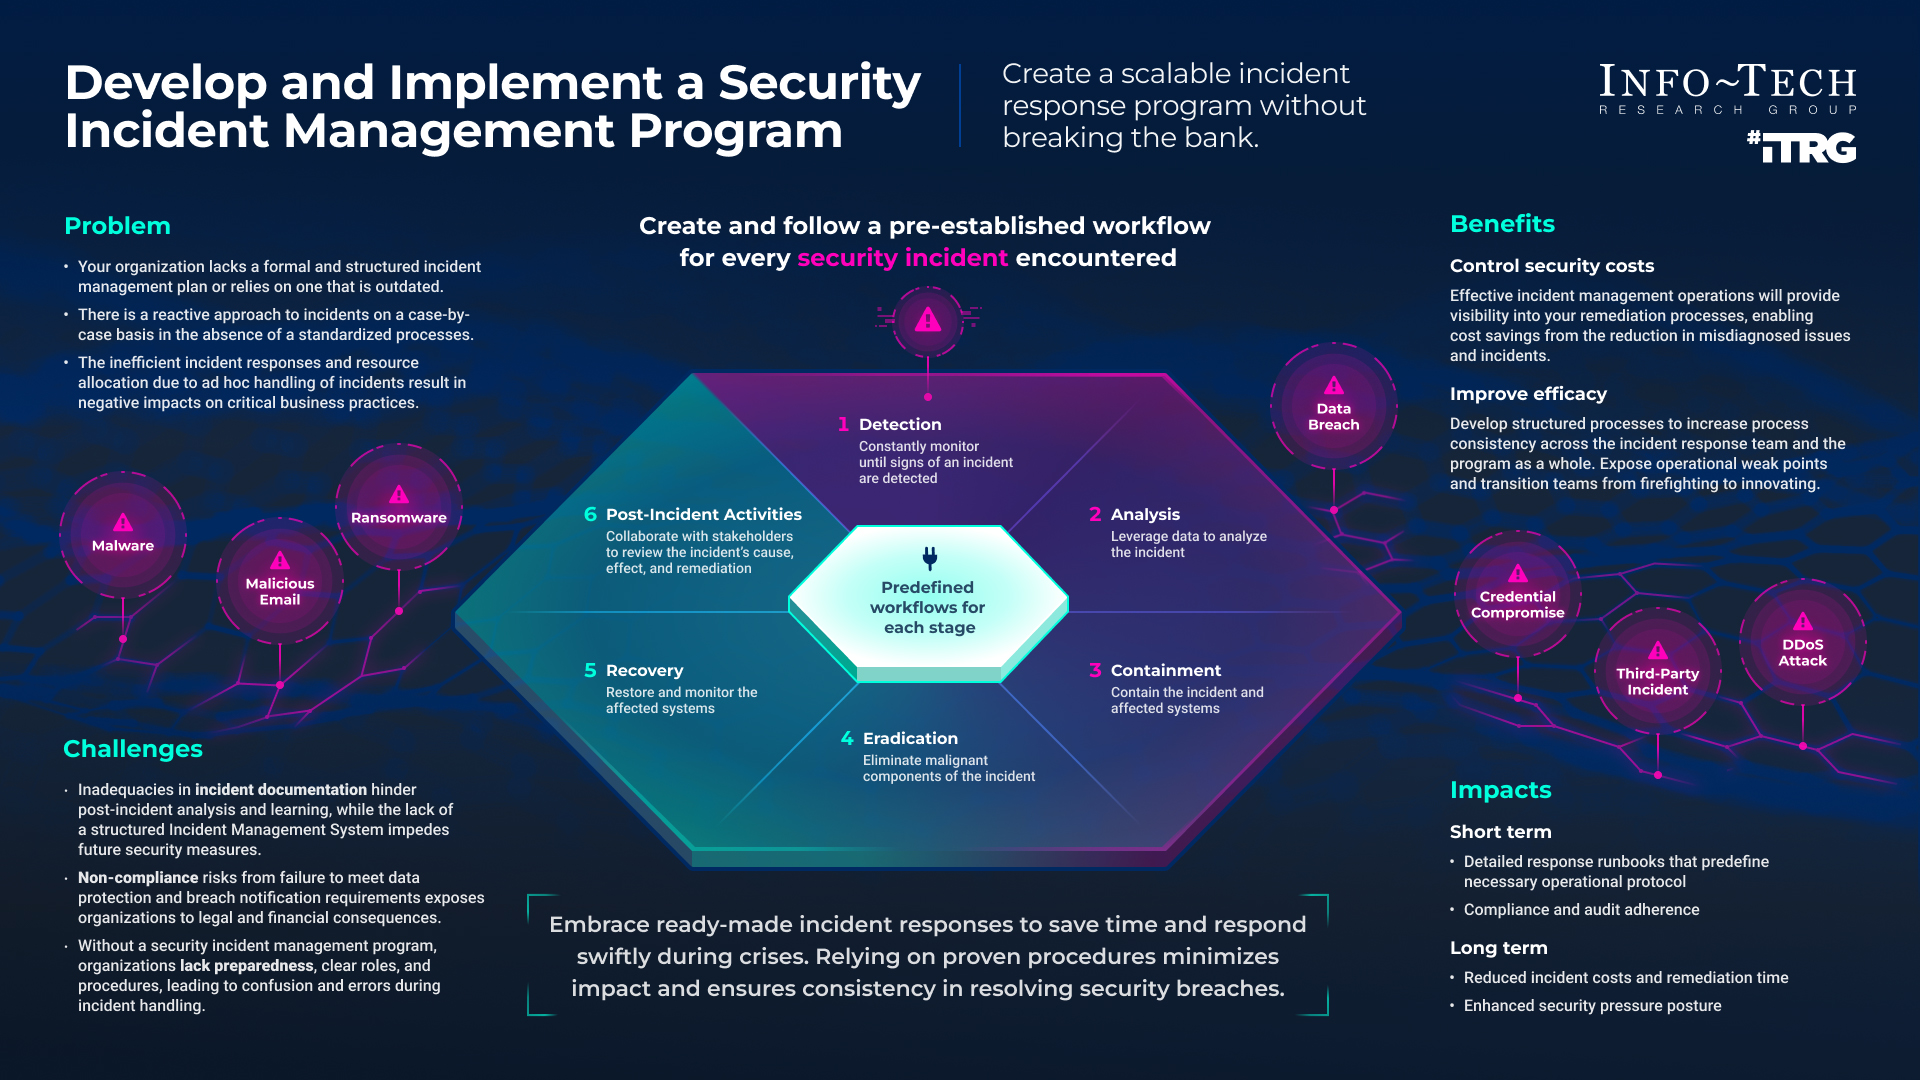
Effective and efficient management of incidents involves a formal process of preparation, detection, analysis, containment, eradication, recovery, and post-incident activities.
This blueprint will walk through the steps of developing a scalable and systematic incident response program relevant to your organization.
Research & Tools
1. Develop and Implement a Security Incident Management Program Deck – A step-by-step document that walks you through how to develop and implement a security incident management program.
Effective and efficient management of incidents involves a formal process of preparation, detection, analysis, containment, eradication, recovery, and post-incident activities. Read our blueprint to find out how to develop and implement a security incident management program, review Info-Tech’s methodology, and understand how we can support you in completing this project.
After each Info-Tech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve. See our top member experiences for this blueprint and what our clients have to say.
9.5/10
Overall Impact
$31,984
Average $ Saved
18
Average Days Saved
Member Testimonials
Client
Northland Power Inc
Experience
Guided Implementation
Impact
10/10
$ Saved
$3,000
Days Saved
5
Testimonial
very helpful advice on revising/updating our cyber security incident response plan.
very helpful advice on revising/updating our cyber security incident response plan.
Member Testimonials
Client
IAMGOLD Corporation
Experience
Guided Implementation
Impact
9/10
$ Saved
N/A
Days Saved
2
Testimonial
InfoTech provided a wide range of practical documentation, templates, and diagrams, complemented by valuable, actionable advice from the consultant...
InfoTech provided a wide range of practical documentation, templates, and diagrams, complemented by valuable, actionable advice from the consultant I worked with, all of which directly supported the successful development of our incident response process.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$68,999
Days Saved
20
Testimonial
My experience has been great so far!!
My experience has been great so far!!
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
10/10
$ Saved
$34,499
Days Saved
20
Testimonial
I now have clarity on who needs to make decisions between IT leadership and organizational leadership. My staff now have a detailed workflow to wor...
I now have clarity on who needs to make decisions between IT leadership and organizational leadership. My staff now have a detailed workflow to work with during a time of crisis.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
9/10
$ Saved
$6,899
Days Saved
10
Testimonial
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$50,000
Days Saved
50
Testimonial
Info-Tech played a key role in shaping our incident response plans by providing valuable feedback and expert guidance throughout the process. Lever...
Info-Tech played a key role in shaping our incident response plans by providing valuable feedback and expert guidance throughout the process. Leveraging their structured approach and best practices ensured our plans were comprehensive and aligned with industry standards. The use of Info-Tech’s templates significantly reduced development time, allowing us to focus on tailoring the content to meet our specific organizational needs. This adaptability not only streamlined the process but also enhanced the overall quality and effectiveness of our incident response strategy. Mike was an invaluable resource, offering insights and support that greatly contributed to the success of this initiative.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$54,400
Days Saved
10
Testimonial
Interaction with a knowledgeable resource to help guide and develop solution for our organization.
Interaction with a knowledgeable resource to help guide and develop solution for our organization.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
9/10
$ Saved
$27,500
Days Saved
10
Testimonial
The best part is that all runbooks are ready to be used, and the advisor is knowledgeable.
The downside is that some tools contain grammatical err...
The best part is that all runbooks are ready to be used, and the advisor is knowledgeable.
The downside is that some tools contain grammatical errors and a few runbooks are missing.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$37,500
Days Saved
16
Testimonial
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
6/10
$ Saved
$13,600
Days Saved
10
Testimonial
Emphasis was placed on hitting time slots for each day's completion rather than on the accuracy and relevance of the information. This despite ulti...
Emphasis was placed on hitting time slots for each day's completion rather than on the accuracy and relevance of the information. This despite ultimately finishing half a day early on Thursday.
The facilitator seemed less sure of his answers, would often either argue the default solution, or ask for an alternative rather than make suggestions. At other times he was seen using ChatCPT to provide answers or to consider points made by the TOGE team. This was noticed and commented on by the IT Director.
Various TOGE documents that had background information on this workshop were provided (e.g. extant ISIRP) at the start of the workshop. There was little reference to those documents made by the facilitator during the workshop. He said he glanced at them but didn't do any deep dives.
The tabletop element itself lasted only two hours and seemed to be more a regurgitation of the documents we had produced in the first three days rather than a roleplay interactive session.
The documentation generated has been provided.
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
9/10
$ Saved
$136K
Days Saved
32
Testimonial
Best -Team collaboration
Worst - Rabbit hole
Best -Team collaboration
Worst - Rabbit hole
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
10/10
$ Saved
$34,000
Days Saved
26
Testimonial
Best part is having the whole suite of incident management references with 2 TTX's accomplished by end of workshop.
Worst part is the minimal st...
Best part is having the whole suite of incident management references with 2 TTX's accomplished by end of workshop.
Worst part is the minimal stakeholder attendance.
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
10/10
$ Saved
$34,000
Days Saved
20
Testimonial
Horia was great to work with on this project.
Horia was great to work with on this project.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$2,584
Days Saved
10
Testimonial
I really enjoyed the interactive nature of the assistance through the case.
I really enjoyed the interactive nature of the assistance through the case.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
N/A
Days Saved
20
Testimonial
Mike was awesome. He was able to help us think through how we could apply your blueprints to existing process, and was also a great sounding board...
Mike was awesome. He was able to help us think through how we could apply your blueprints to existing process, and was also a great sounding board for helping think through some of the resistances we've been experiencing to changes in the style and approach of these documents.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
9/10
$ Saved
$10,000
Days Saved
10
Testimonial
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$13,600
Days Saved
10
Testimonial
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
9/10
$ Saved
$21,760
Days Saved
14
Testimonial
Mike was able to immediately address our needs by providing straight to the point assistance. I would be happy to get help again in the future.
Mike was able to immediately address our needs by providing straight to the point assistance. I would be happy to get help again in the future.
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
10/10
$ Saved
$34,000
Days Saved
10
Testimonial
A big thank you to Horia for the outstanding job facilitating the security incident workshop and tabletop exercise. Your expertise and guidance mad...
A big thank you to Horia for the outstanding job facilitating the security incident workshop and tabletop exercise. Your expertise and guidance made the session informative and impactful, providing valuable insights for all participants, from frontline support to Infrastructure and DevOps teams. We look forward to future collaborations!
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$68,000
Days Saved
23
Testimonial
Petars insight into security and governance has really made a difference in our posture and preparedness. We can purchase solutions all day but not...
Petars insight into security and governance has really made a difference in our posture and preparedness. We can purchase solutions all day but not knowing what you don't know makes one's effort ineffective
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$34,000
Days Saved
10
Testimonial
Petar Hristov did a phenomenal job of walking us through the Develop and Implement a Security Incident Management Program. His advice was extremely...
Petar Hristov did a phenomenal job of walking us through the Develop and Implement a Security Incident Management Program. His advice was extremely helpful. Having worked with many Info-Tech Analysts over the years, I have to say that Petar was one of the most effective that I've ever had the pleasure of collaborating with.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$3,179
Days Saved
5
Testimonial
It was easy to engage with InfoTech.
Also the security management blueprint from InfoTech was the closest to my requirements.
It was easy to engage with InfoTech.
Also the security management blueprint from InfoTech was the closest to my requirements.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
9/10
$ Saved
$12,240
Days Saved
14
Testimonial
It's all laid out for you and ready to modify as needed. Our SME was very knowledgeable and patient with our team.
It's all laid out for you and ready to modify as needed. Our SME was very knowledgeable and patient with our team.
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
9/10
$ Saved
N/A
Days Saved
35
Testimonial
The best parts of the experience was the customization of the workshop to meet our needs. This was accomplished through preparatory calls as well ...
The best parts of the experience was the customization of the workshop to meet our needs. This was accomplished through preparatory calls as well as a thorough understanding of the unique environment. The worst part of the experience is the realization of the necessary follow-on efforts that will be needed to successfully adapt the deliverables. More knowledge requires more work.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
8/10
$ Saved
$1,700
Days Saved
2
Testimonial
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$34,250
Days Saved
10
Testimonial
The personal connection with an analyst.
The personal connection with an analyst.
Member Testimonials
Client
Member Organization
Experience
Workshop
Impact
9/10
$ Saved
$50,000
Days Saved
14
Testimonial
The best part was coming together as a consortium and forcing ourselves, with Horia's assistance to dedicate the time to complete this incredibly i...
The best part was coming together as a consortium and forcing ourselves, with Horia's assistance to dedicate the time to complete this incredibly important task. We are much further along than we were before.
The worst part was even though we accomplished so much, the workshop really did indicate how much further we have to go.
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$32,195
Days Saved
10
Testimonial
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
$13,700
Days Saved
105
Testimonial
Willingness to provide guidance and followup
Willingness to provide guidance and followup
Member Testimonials
Client
Member Organization
Experience
Guided Implementation
Impact
10/10
$ Saved
N/A
Days Saved
20
Testimonial
Robert is very knowledgeable providing practical advice and guidance. The facilitation of the tabletop exercise was a beneficial exercise to complete.
Robert is very knowledgeable providing practical advice and guidance. The facilitation of the tabletop exercise was a beneficial exercise to complete.
Member Testimonials
Client
Experience
Impact
$ Saved
Days Saved
Testimonial
Northland Power Inc
Guided Implementation
10/10
$3,000
5
very helpful advice on revising/updating our cyber security incident response plan.
very helpful advice on revising/updating our cyber security incident response plan.
IAMGOLD Corporation
Guided Implementation
9/10
N/A
2
InfoTech provided a wide range of practical documentation, templates, and diagrams, complemented by valuable, actionable advice from the consultant...
InfoTech provided a wide range of practical documentation, templates, and diagrams, complemented by valuable, actionable advice from the consultant I worked with, all of which directly supported the successful development of our incident response process.
Member Organization
Guided Implementation
10/10
$68,999
20
My experience has been great so far!!
My experience has been great so far!!
Member Organization
Workshop
10/10
$34,499
20
I now have clarity on who needs to make decisions between IT leadership and organizational leadership. My staff now have a detailed workflow to wor...
I now have clarity on who needs to make decisions between IT leadership and organizational leadership. My staff now have a detailed workflow to work with during a time of crisis.
Member Organization
Guided Implementation
9/10
$6,899
10
Member Organization
Guided Implementation
10/10
$50,000
50
Info-Tech played a key role in shaping our incident response plans by providing valuable feedback and expert guidance throughout the process. Lever...
Info-Tech played a key role in shaping our incident response plans by providing valuable feedback and expert guidance throughout the process. Leveraging their structured approach and best practices ensured our plans were comprehensive and aligned with industry standards. The use of Info-Tech’s templates significantly reduced development time, allowing us to focus on tailoring the content to meet our specific organizational needs. This adaptability not only streamlined the process but also enhanced the overall quality and effectiveness of our incident response strategy. Mike was an invaluable resource, offering insights and support that greatly contributed to the success of this initiative.
Member Organization
Guided Implementation
10/10
$54,400
10
Interaction with a knowledgeable resource to help guide and develop solution for our organization.
Interaction with a knowledgeable resource to help guide and develop solution for our organization.
Member Organization
Guided Implementation
9/10
$27,500
10
The best part is that all runbooks are ready to be used, and the advisor is knowledgeable.
The downside is that some tools contain grammatical err...
The best part is that all runbooks are ready to be used, and the advisor is knowledgeable.
The downside is that some tools contain grammatical errors and a few runbooks are missing.
Member Organization
Guided Implementation
10/10
$37,500
16
Member Organization
Workshop
6/10
$13,600
10
Emphasis was placed on hitting time slots for each day's completion rather than on the accuracy and relevance of the information. This despite ulti...
Emphasis was placed on hitting time slots for each day's completion rather than on the accuracy and relevance of the information. This despite ultimately finishing half a day early on Thursday.
The facilitator seemed less sure of his answers, would often either argue the default solution, or ask for an alternative rather than make suggestions. At other times he was seen using ChatCPT to provide answers or to consider points made by the TOGE team. This was noticed and commented on by the IT Director.
Various TOGE documents that had background information on this workshop were provided (e.g. extant ISIRP) at the start of the workshop. There was little reference to those documents made by the facilitator during the workshop. He said he glanced at them but didn't do any deep dives.
The tabletop element itself lasted only two hours and seemed to be more a regurgitation of the documents we had produced in the first three days rather than a roleplay interactive session.
The documentation generated has been provided.
Member Organization
Workshop
9/10
$136K
32
Best -Team collaboration
Worst - Rabbit hole
Best -Team collaboration
Worst - Rabbit hole
Member Organization
Workshop
10/10
$34,000
26
Best part is having the whole suite of incident management references with 2 TTX's accomplished by end of workshop.
Worst part is the minimal st...
Best part is having the whole suite of incident management references with 2 TTX's accomplished by end of workshop.
Worst part is the minimal stakeholder attendance.
Member Organization
Workshop
10/10
$34,000
20
Horia was great to work with on this project.
Horia was great to work with on this project.
Member Organization
Guided Implementation
10/10
$2,584
10
I really enjoyed the interactive nature of the assistance through the case.
I really enjoyed the interactive nature of the assistance through the case.
Member Organization
Guided Implementation
10/10
N/A
20
Mike was awesome. He was able to help us think through how we could apply your blueprints to existing process, and was also a great sounding board...
Mike was awesome. He was able to help us think through how we could apply your blueprints to existing process, and was also a great sounding board for helping think through some of the resistances we've been experiencing to changes in the style and approach of these documents.
Member Organization
Guided Implementation
9/10
$10,000
10
Member Organization
Guided Implementation
10/10
$13,600
10
Member Organization
Guided Implementation
9/10
$21,760
14
Mike was able to immediately address our needs by providing straight to the point assistance. I would be happy to get help again in the future.
Mike was able to immediately address our needs by providing straight to the point assistance. I would be happy to get help again in the future.
Member Organization
Workshop
10/10
$34,000
10
A big thank you to Horia for the outstanding job facilitating the security incident workshop and tabletop exercise. Your expertise and guidance mad...
A big thank you to Horia for the outstanding job facilitating the security incident workshop and tabletop exercise. Your expertise and guidance made the session informative and impactful, providing valuable insights for all participants, from frontline support to Infrastructure and DevOps teams. We look forward to future collaborations!
Member Organization
Guided Implementation
10/10
$68,000
23
Petars insight into security and governance has really made a difference in our posture and preparedness. We can purchase solutions all day but not...
Petars insight into security and governance has really made a difference in our posture and preparedness. We can purchase solutions all day but not knowing what you don't know makes one's effort ineffective
Member Organization
Guided Implementation
10/10
$34,000
10
Petar Hristov did a phenomenal job of walking us through the Develop and Implement a Security Incident Management Program. His advice was extremely...
Petar Hristov did a phenomenal job of walking us through the Develop and Implement a Security Incident Management Program. His advice was extremely helpful. Having worked with many Info-Tech Analysts over the years, I have to say that Petar was one of the most effective that I've ever had the pleasure of collaborating with.
Member Organization
Guided Implementation
10/10
$3,179
5
It was easy to engage with InfoTech.
Also the security management blueprint from InfoTech was the closest to my requirements.
It was easy to engage with InfoTech.
Also the security management blueprint from InfoTech was the closest to my requirements.
Member Organization
Guided Implementation
9/10
$12,240
14
It's all laid out for you and ready to modify as needed. Our SME was very knowledgeable and patient with our team.
It's all laid out for you and ready to modify as needed. Our SME was very knowledgeable and patient with our team.
Member Organization
Workshop
9/10
N/A
35
The best parts of the experience was the customization of the workshop to meet our needs. This was accomplished through preparatory calls as well ...
The best parts of the experience was the customization of the workshop to meet our needs. This was accomplished through preparatory calls as well as a thorough understanding of the unique environment. The worst part of the experience is the realization of the necessary follow-on efforts that will be needed to successfully adapt the deliverables. More knowledge requires more work.
Member Organization
Guided Implementation
8/10
$1,700
2
Member Organization
Guided Implementation
10/10
$34,250
10
The personal connection with an analyst.
The personal connection with an analyst.
Member Organization
Workshop
9/10
$50,000
14
The best part was coming together as a consortium and forcing ourselves, with Horia's assistance to dedicate the time to complete this incredibly i...
The best part was coming together as a consortium and forcing ourselves, with Horia's assistance to dedicate the time to complete this incredibly important task. We are much further along than we were before.
The worst part was even though we accomplished so much, the workshop really did indicate how much further we have to go.
Member Organization
Guided Implementation
10/10
$32,195
10
Member Organization
Guided Implementation
10/10
$13,700
105
Willingness to provide guidance and followup
Willingness to provide guidance and followup
Member Organization
Guided Implementation
10/10
N/A
20
Robert is very knowledgeable providing practical advice and guidance. The facilitation of the tabletop exercise was a beneficial exercise to complete.
Robert is very knowledgeable providing practical advice and guidance. The facilitation of the tabletop exercise was a beneficial exercise to complete.
Workshop
Develop and Implement a Security Incident Management Program Workshop
Work with our analysts to accelerate this project using Info-Tech's proven workshop approach.
Module 1: Prepare Your Incident Response Program
The Purpose
Understand the purpose of incident response.
Formalize the program.
Identify key players and escalation points.
Key Benefits Achieved
Common understanding of the importance of incident response.
Various business units becoming aware of their roles in the incident management program.
Formalized documentation.
Activities
Outputs
1.1
Assess the current process, obligations, scope, and boundaries of the incident management program.
Outputs
Understanding of the incident landscape
1.2
Identify key players for the response team and for escalation points.
Outputs
An identified incident response team
1.3
Formalize documentation.
Outputs
A security incident management charter
A security incident management policy
1.4
Prioritize incidents requiring preparation.
Outputs
A list of top-priority incidents
A general security incident management plan
A security incident response RACI chart
Module 2: Develop Incident-Specific Runbooks
The Purpose
Document the clear response procedures for
top-priority incidents.
Key Benefits Achieved
As incidents occur, clear response procedures are documented for efficient and effective recovery.
Activities
Outputs
2.1
For each top-priority incident, document the workflow from detection through analysis, containment, eradication, recovery, and post-incident analysis.
Outputs
Up to five incident-specific runbooks
Module 3: Maintain and Optimize the Program
The Purpose
Ensure the response procedures are realistic and effective.
Identify key metrics to measure the success of the program.
Key Benefits Achieved
Real-time run-through of security incidents to ensure roles and responsibilities are known.
Understanding of how to measure the success of the program.
Activities
Outputs
3.1
Limited scope tabletop exercise.
Outputs
Completed tabletop exercise
3.2
Discuss key metrics.
Outputs
Key success metrics identified
Develop and Implement a Security Incident Management Program
Create a scalable incident response program without breaking the bank.
Analyst perspective
In today’s digital landscape, security incidents are an unavoidable reality for organizations, regardless of their size or industry. From data breaches and ransomware attacks to insider threats and phishing scams, the range of security incidents keeps growing. This demands a proactive and robust approach to security incidents.
Organizations with formalized incident response plans contain incidents faster and benefit from significant cost savings as a result. When faced with a security incident, organizations cannot afford to waste time deliberating how to respond and must have designated roles and responsibilities so that everyone can act decisively.
As well, organizations need to track and measure key performance indicators (KPIs) such as response time, success rate, and recovery time regularly. Tracking these KPIs can provide valuable insights for continuous improvement and can fine-tune response strategies.
Ultimately, a proactive security incident management approach empowers organizations to navigate security incidents with confidence and mitigate potential consequences swiftly when an incident occurs.
Seva Ioussoufovitch Senior Research Analyst Infotech
Executive summary
Your Challenge
Security incidents are inevitable, but how they’re dealt with can make or break an organization. A poor incident response negatively affects business practices, including workflow, revenue generation, and public image.
The incident response of most organizations is ad hoc, at best. A formal management plan is rarely developed or adhered to, resulting in ineffective firefighting responses and an inefficient allocation of resources.
Common Obstacles
Tracked incidents are often classified using ready-made responses that are not necessarily applicable to an organization. With so many classifications, tracking becomes inefficient and indigestible, allowing major incidents to fall through the cracks.
As well, outcomes of incident-response tactics may not be formally tracked or communicated, resulting in the lack of a comprehensive understanding of trends and patterns regarding incidents. This may lead to an organization being revictimized by the same vector.
However, even having a formal incident response document to meet compliance requirements is not useful if no one is adhering to it.
Info-Tech’s Approach
Effective and efficient management of incidents involves a formal process of preparation, detection, analysis, containment, eradication, recovery, and post-incident activities.
This blueprint will walk you through the steps of developing a scalable and systematic incident response program that is relevant to your organization.
Infotech Insight
Embrace the use of ready-made responses when handling incidents. These pre-established response plans can save valuable time and effort during a crisis. By relying on proven and tested procedures, your team can respond swiftly and efficiently, minimizing the impact of incidents and ensuring a consistent approach to resolving security breaches.
Challenges of inadequate security incident management
Lack of preparedness: A security incident management program helps to prepare your organization for potential security incidents by establishing clear roles, responsibilities, and procedures. Without such a program, your team may be ill-prepared to handle incidents, resulting in confusion, chaos, and a higher likelihood of errors or mistakes during the response.
Incomplete incident documentation: It is important to ensure that incidents are properly documented and there are measures for dealing with and resolving them. Without an incident management system, your organization may not have the structures to report and document incidents, which could impede root-cause identification, post-incident analysis, and the ability to learn from previous incidents in order to enhance future security measures.
Regulatory noncompliance: Some industries have specific regulations and legal requirements for incident management, data protection, and breach notification. Without an updated plan that reflects these regulations and requirements, your organization may fail to meet compilatory needs, which could lead to regulatory consequences, financial sanctions, or even a bad reputation.
181 days — Mean time to identify a data breach
60 days — Mean time to contain a data breach
(Source: “Cost of a Data Breach Report 2025,” IBM, 2025)
Defining incident and event terminology
IT Incident
An IT incident is any event that is not part of the standard operation of a service and that causes, or may cause, an interruption to, or a reduction in, the quality of this service.
Security Event
A security event is any event or occurrence that could potentially have information security implications.
For example, a spam email is a security event because it may contain links to malware.
Organizations may be hit with thousands, or perhaps millions, of identifiable security events each day.
These security events are typically handled by automated tools or simply logged.
Security Incident
A security incident is a security event that results in damage, such as lost data.
A security incident can also be a security event that does not involve damage but is a viable risk.
For example, an employee clicking on a link in a spam email that made it through filters may be viewed as a security incident.
It’s not a matter of if you will have a security incident, but when
Threats keep evolving and breach costs remain steep, but an effective response plan helps keep incidents manageable. Prepare for the inevitable with an incident response program.
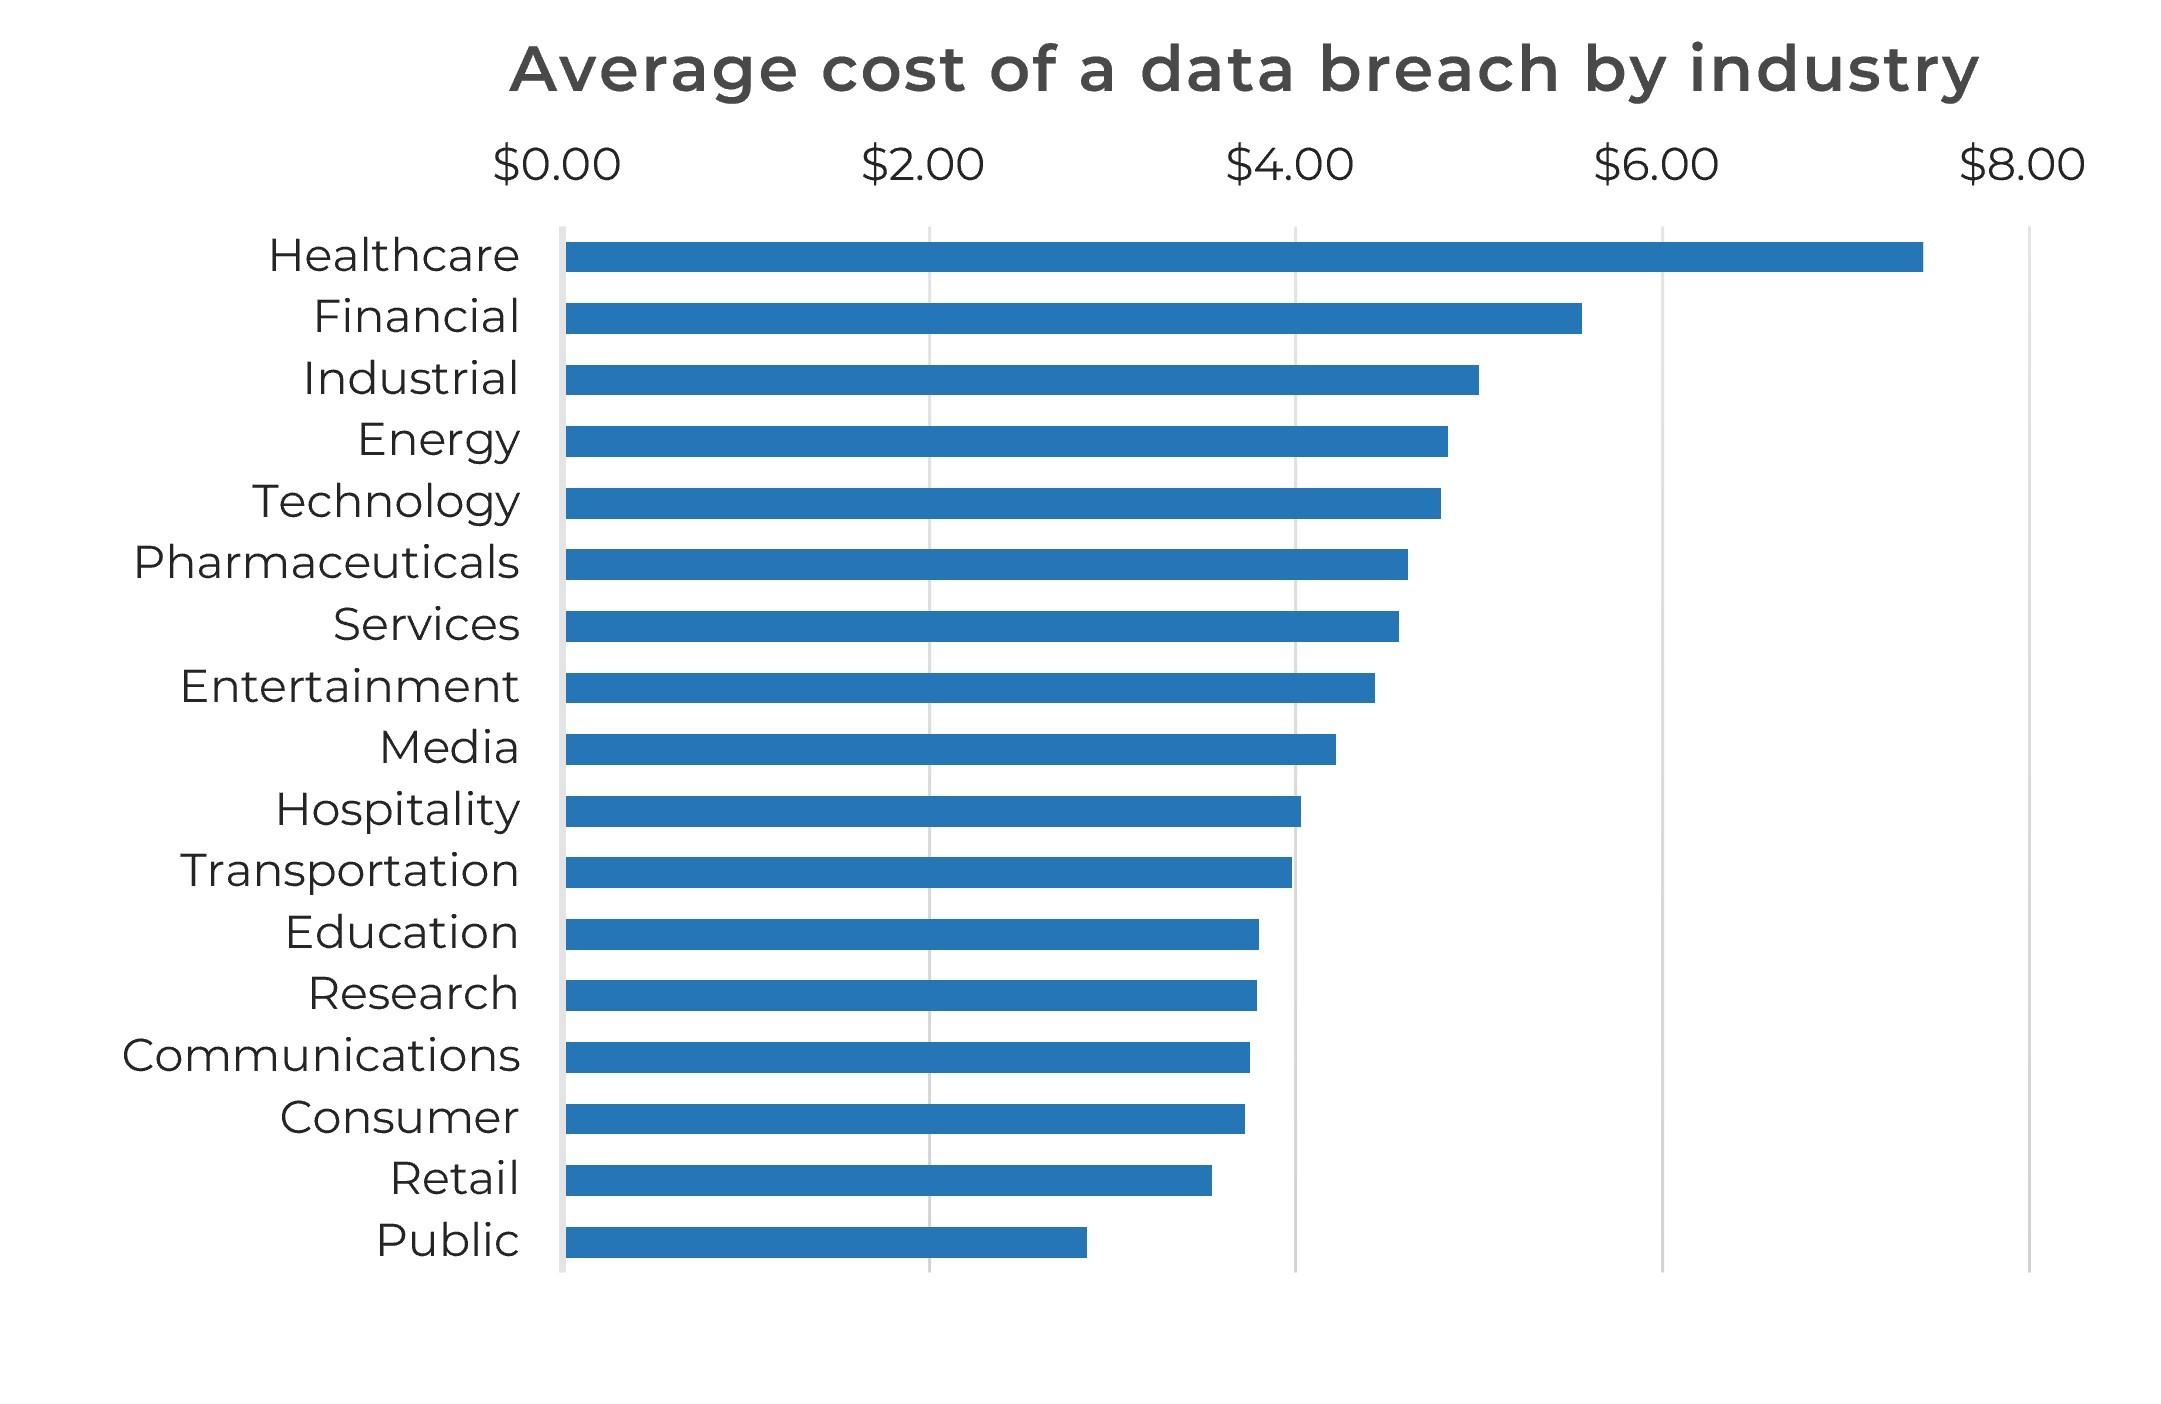
The average cost per data breach was US$4.44 million globally but US$10.22 million for US organizations. This record cost was partially driven by higher regulatory fines and detection/escalation costs.
Data breaches involving multiple environments accounted for 30% of breaches and had an average breach cost of US$5.05 million.
The average breach cost savings at organizations that identified and contained a breach in less than 200 days was US$1.14 million.
20% of security incidents involve shadow AI, and 13% of organizations have experienced an AI-related security incident.
32% of organizations paid a regulatory fine due to a data breach.
(Source: “Cost of a Data Breach Report 2025,” IBM, 2025)
This research is designed for a chief information security officer (CISO) who is dealing with:
Inefficient use of time and money when retroactively responding to incidents that negatively affect business revenue and workflow.
Resistance from management to adequately develop a formal incident response plan.
Lack of closure of incidents, resulting in being revictimized by the same vector.
This research will also assist business stakeholders who are responsible for:
Improving workflow and managing operations in the event of a security incident to reduce any adverse business impacts.
Ensuring that incident response compliance requirements are being adhered to.
Benefits of an incident management program
Effective incident management will help you…
Improve efficacy. Develop structured processes to increase process consistency across the incident response team and the program as a whole. Expose operational weak points, and transition teams from firefighting to innovating.
Improve threat detection, prevention, analysis, and response. Enhance your pressure posture through a structured and intelligence-driven incident handling and remediation framework.
Improve visibility and information sharing. Promote both internal and external information sharing to enable good decision making.
Create and clarify accountability and responsibility. Establish a clear level of accountability throughout the incident response program and ensure role responsibility for all tasks and processes involved in service delivery.
Control security costs. Establish effective incident management operations to provide visibility into your remediation processes, enabling cost savings from misdiagnosed issues and incident reduction.
Identify opportunities for continuous improvement. Increase visibility into current performance levels and accurately identify opportunities for continuous improvement with a holistic measurement program.
Short-Term Impact
Streamlined security incident management program
Formalized and structured response process
Comprehensive list of operational gaps and initiatives
Detailed response runbooks that predefine necessary operational protocol
Compliance and audit adherence
Long-Term Impact
Reduced incident costs and remediation time
Increased operational collaboration between prevention, detection, analysis, and response efforts
Enhanced security pressure posture
Improved communication with executives about relevant security risks to the business
Preserved reputation and brand equity
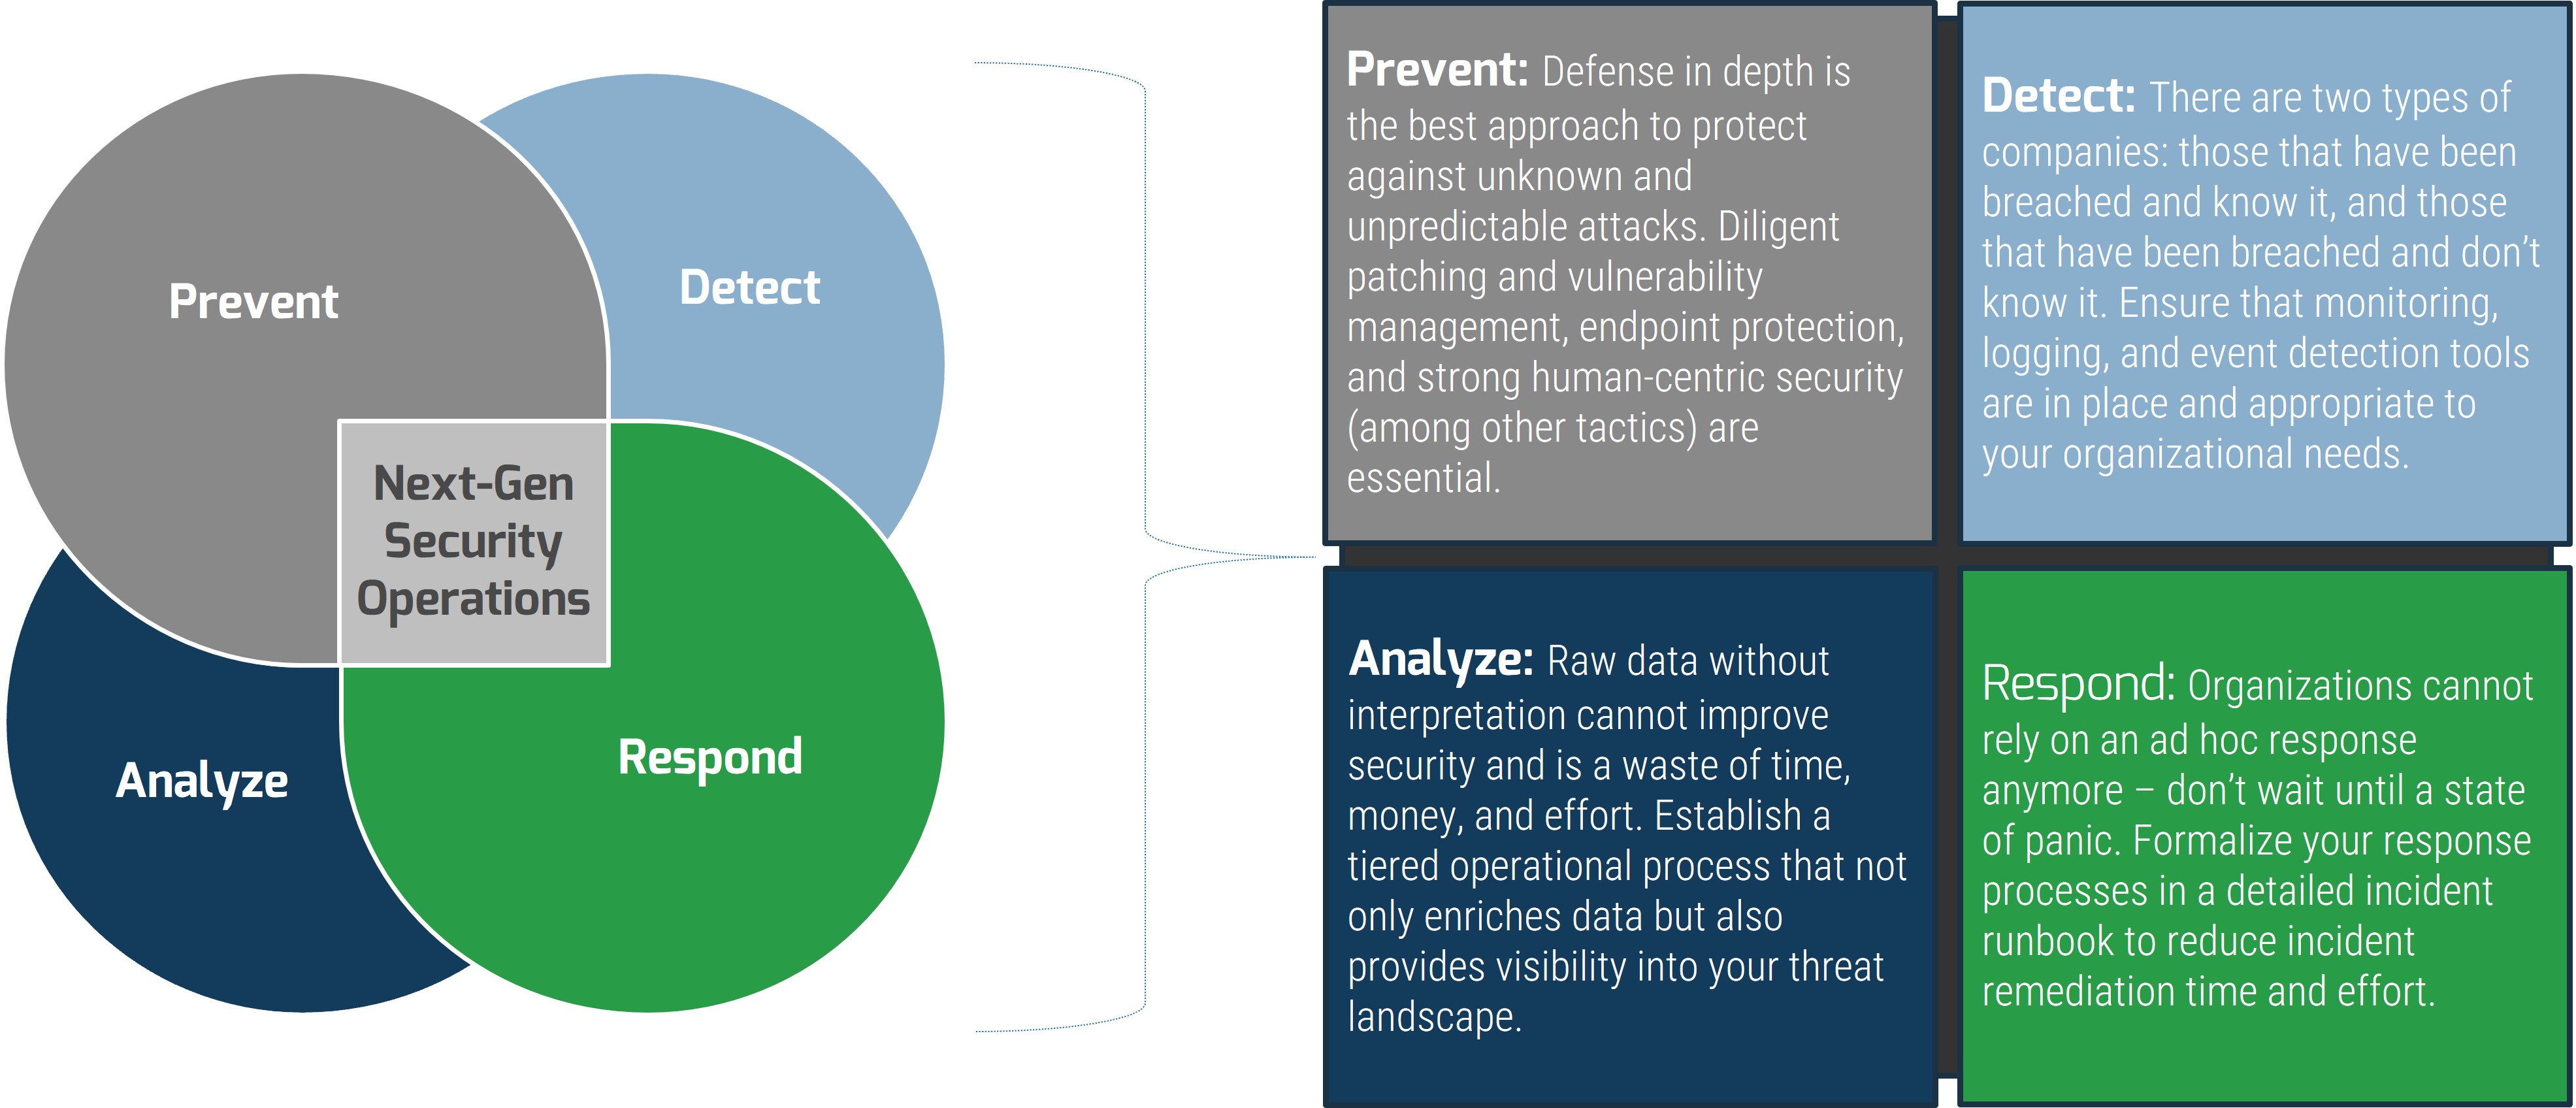
Maintain a holistic security operations program
Prevent: Defense in depth is the best approach to protect against unknown and unpredictable attacks. Diligent patching and vulnerability management, endpoint protection, and strong human-centric security (among other tactics) are essential.
Detect: There are two types of companies: those that have been breached and know it, and those that have been breached and don’t know it. Ensure that monitoring, logging, and event detection tools are in place and appropriate to your organizational needs.
Analyze: Raw data without interpretation cannot improve security and is a waste of time, money, and effort. Establish a tiered operational process that not only enriches data but also provides visibility into your threat landscape.
Respond: Organizations cannot rely on an ad hoc response anymore – don’t wait until a state of panic. Formalize your response processes in a detailed incident runbook to reduce incident remediation time and effort.
Insight Breakdown
Save your organization response time and confusion by developing your own incident use cases.
Out-of-the-box incident classifications often offer too many irrelevant cases, not applicable to your organization, making it difficult to sift through all the incidents to find the cases you care about. Develop specific incident use cases that correspond to relevant incidents in order to identify the response process quickly and eliminate ambiguity when cases are handled by different individuals.
Know when incidents are beyond the scope of your use cases. Identify when to seek third-party assistance, and have contractors on retainer so you are not shopping around during a crisis. Prepare as much as possible before issues arise.
Document and track each step of incident handling through the Operate phase.
A thorough and comprehensive record of an incident’s lifecycle will help with understanding the root cause and allow for faster remediation of any future reoccurrence of the incident. It will also support any legal escalation. Tracking the cost of work hours helps with determining the overall impact on the organization.
Results of each incident response must be analyzed, tracked, and reviewed regularly. Otherwise, the lack of a comprehensive understanding of incident trends and patterns will lead to being revictimized by the same vector.
Work collaboratively and maintain consistent communication both internally and externally.
Pre-emptively reserve multiple secure channels of communication to guarantee uncompromised methods of communication during incident response.
Work together with other organizations to share information and take advantage of intel gathered about incoming threats in the industry. Effective communication is a fundamental instrument for successful incident management.
Do not wait for a state of panic to organize communication tactics. Have public relations plans and third-party contracts with minimal update requirements established prior to experiencing an incident.
Blueprint deliverables
Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals.
Key deliverable:
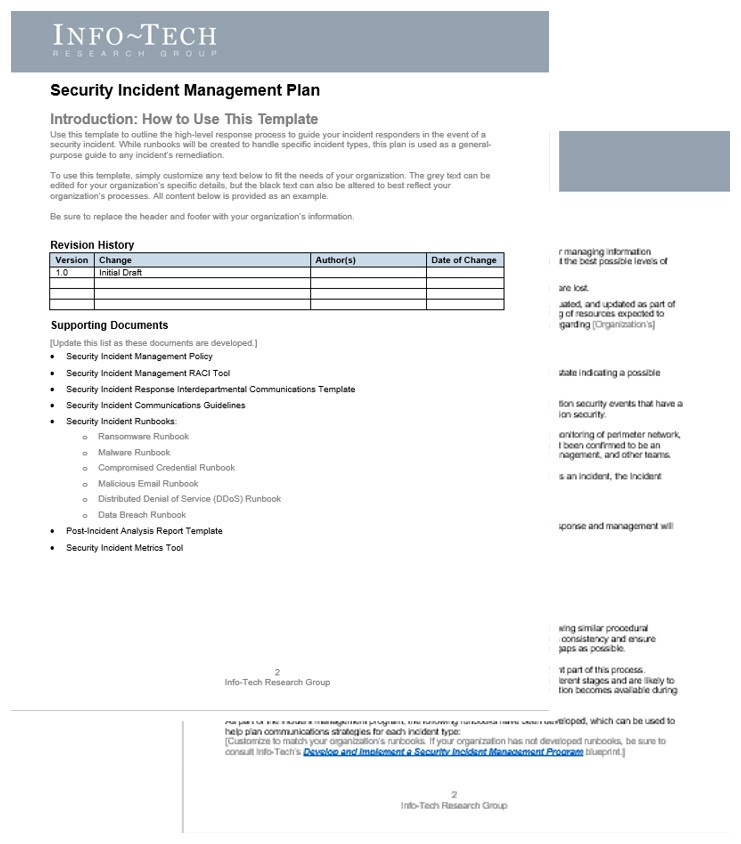
Security Incident Management Plan
A central, high-level document to describe goals, roles, and responsibilities, and provide evidence to auditors that a process has been developed and formalized.
Emergency Contact and Communication Guide Template
Manage and Improve Incident Management
Security Incident Report Template
Security Incident Metrics Tool
Act Efficiently and Effectively
Security Incident Runbook Prioritization Tool
Security Incident Management Runbooks
Security Incident Management Workflows
Infotech’s methodology to develop and implement a security incident management program
1. Prepare
2. Operate
3. Maintain and Optimize
Phase Steps
1.1 Establish the drivers, challenges, and benefits of completing this project. 1.2 Understand why your organization should focus on security incident management. 1.3 Identify key players for security incident management. 1.4 Develop a security incident management policy. 1.5 Develop a security incident management plan.
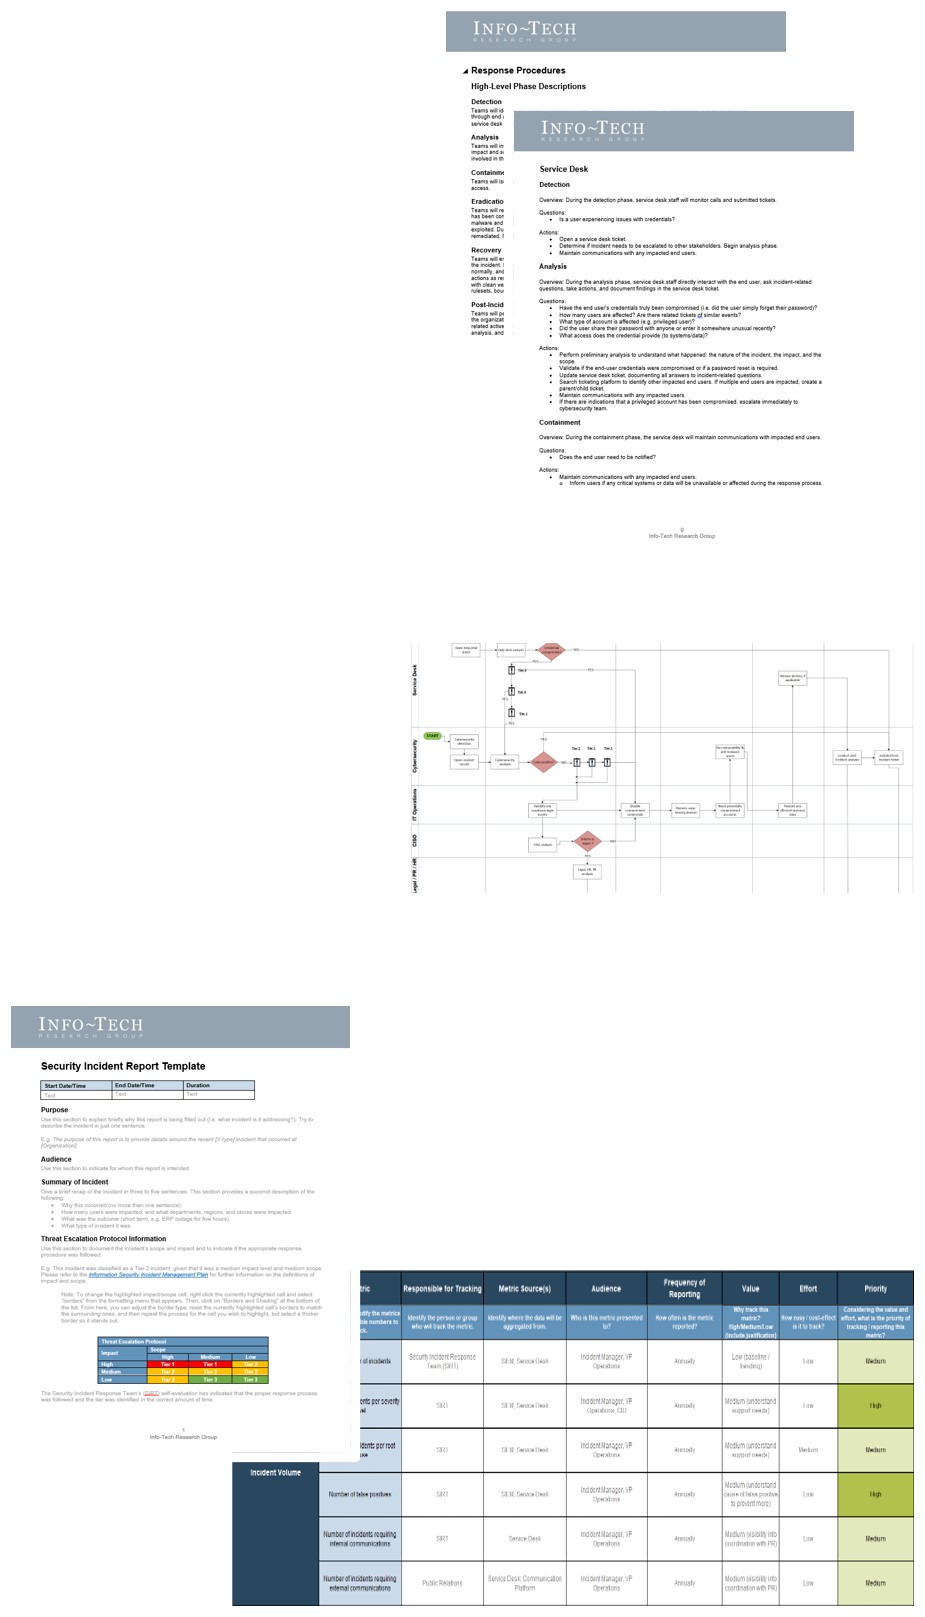
2.1 Understand the security incident management framework. 2.2 Understand the purpose of runbooks. 2.3 Prioritize the development of incident-specific runbooks. 2.4.1 Use operational flowcharts to illustrate your response procedures. 2.4.2 Create runbooks that align with your response workflows. 2.5 Complete the Security Incident Report Template.
3.1 Conduct simulated exercises. 3.2 Assess and optimize your security incident management program over time.
Phase Outcomes
Phase 1 outcomes:
Security Incident Management Maturity Checklist
Security Incident Management RACI Tool
Security Incident Management Policy Template
Security Incident Management Plan
Phase 2 outcomes:
Prioritized list of incident-specific workflows
Detailed runbooks for top-priority incidents
Security Incident Report Template
Phase 3 outcomes:
Formalized tracking system for benchmarking security incident metrics
Areas of improvement for your security incident management program.
Measure the value of this blueprint
Guided Implementation
Purpose
Measured Value
Phase 1: Prepare
Understand the need for an incident response program.
Develop your incident response policy and plan.
Develop classifications around incidents.
Establish your program implementation roadmap.
Time, value, and resources saved using our classification guidance and templates: 2 FTEs*2 days*$80,000/year = $1,280
Time, value, and resources saved using our classification guidance and templates: 2 FTEs*5 days*$80,000/year = $3,200
Phase 2: Operate
Prioritize runbooks and develop the processes to create your own incident response program:
Detect
Analyze
Contain
Eradicate
Recover
Conduct Post-Incident Activities
Time, value, and resources saved using our guidance: 4 FTEs*10 days*$80,000/year = $12,800 (if done internally)
Time, value, and resources saved using our guidance: 1 consultant*15 days*$2,000/day = $30,000 (if done by third party)
Phase 3: Maintain and Optimize
Develop methods for proper reporting and create templates for communicating incident response to key parties.
Time, value, and resources saved using our guidance, templates, and tabletop exercises:
2 FTEs*3 days*$80,000/year = $1,920
Total Costs
Just to get an incident response program off the ground
$49,200
After each Infotech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve.
Marks & Spencer (M&S) and the Co-op Group, two of the United Kingdom’s top retailers, were both attacked by the same threat actor within days of each other in April 2025. In both cases, social engineering was the attack vector that allowed attackers to breach the organizations.
Co-op detected the threat within minutes and had initiated their full incident management process within the day. On the other hand, M&S only detected the breach after two days, once attackers had already deployed ransomware in their environment.
Beyond quick detection, Co-op had updated and well-rehearsed incident runbooks that were leveraged across the organization. While M&S also had incident management capabilities in place, the scale and speed of the attack overwhelmed their response capacity.
Results
Co-op’s back-office operations were disrupted and 6.5 million member records were exposed; however, Co-op’s customer-facing services experienced limited disruption. Co-op estimated an £80M loss in operating profit due to the incident.
M&S had to bring down large segments of their environment; online orders were suspended for weeks for an estimated profit impact of £300M.
Co-op’s formalized incident response program, coupled with well-practiced runbooks, were critical in helping them greatly limit the potential damage of the incident.
Infotech Insight
By the time an incident occurs, gaps in your incident management program may cost you millions. A strong program delivers measurable value by preserving operational continuity and limiting financial loss.
Develop and Implement a Security Incident Management Program
Phase 1
Prepare
Phase 1
Phase 2
Phase 3
Prepare
Operate
Maintain and Optimize
This phase will walk you through the following steps:
1.1 Establish the drivers, challenges, and benefits of completing this project.
1.2 Understand why your organization should focus on security incident management.
1.3 Identify key players for security incident management.
1.4 Develop a security incident management policy.
1.5 Develop a security incident management plan.
1.1 Establish the drivers, challenges, and benefits of completing this project
Don’t let your pain points and blockers keep you from the many benefits of security incident management.
Drivers
What problems and threats are you currently facing because you do not follow a formal process for incident management?
Typical pain points include:
High susceptibility to risk
Costly repairs to damaged and lost assets
Downtime of resources
Time and effort wasted retroactively patching preventable security issues
Legal and compliance ramifications
Reputational damage
Challenges
Why has this new project not yet been started? What is stopping management from getting on board?
Typical challenges include:
Time constraints
Budget constraints
Operational disruption
Lack of explicit return on investment (ROI)
Overconfidence: “We have the best technical defenses, so we won’t face harmful incidents.”
Benefits
What will the business gain from developing and following an incident response plan? The benefits must outweigh the blockers for the plan to be worthwhile.
Typical benefits include:
↓ Outages and downtime
↓ Repeated/recurring incidents
↓ Reputation damage
↑ Protection of assets
↑ Productivity
↑ Regulatory compliance
↑ Preparedness
↑ User satisfaction
1.2 Understand why your organization should focus on security incident management
An ineffective incident management process can lead to lost productivity, more downtime, and higher support costs.
Poor Incident Management
Incident resolution takes too long.
When incident fixes take too long, downtime increases and user productivity decreases, potentially creating a negative impact on revenue generation.
Incidents do not get fixed properly initially.
Confusion over process and lack of expertise limits successful resolution, resulting in outages and lost productivity.
Incidents get escalated too quickly.
Every escalation increases costs exponentially. You must determine when it is absolutely necessary to escalate.
Incidents are not prioritized correctly at intake.
Resources are not allocated to the most urgent issues. Breaches may be missed while minor incidents with low business impact are addressed.
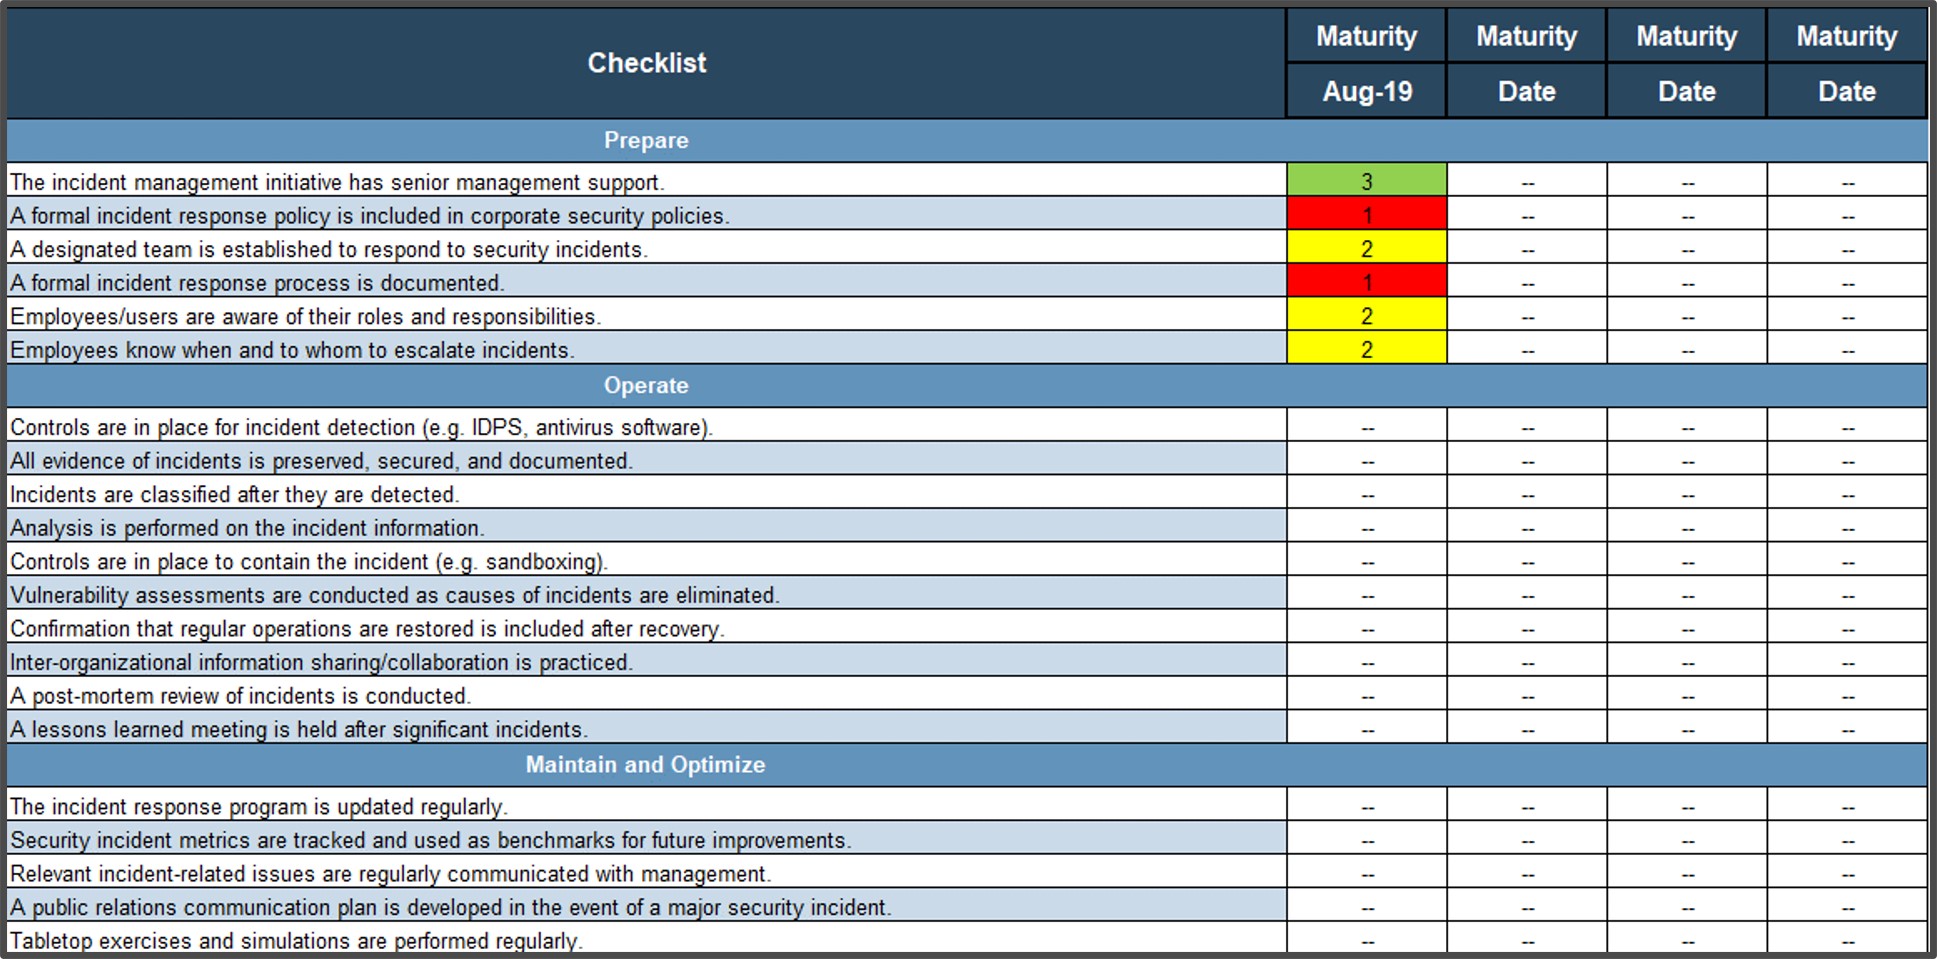
Complete the Security Incident Management Maturity Checklist
Quickly gauge your current process with a security incident management checklist.
While not every measure is essential to a successful incident management process, substantial gaps indicate where improvements to incident management are required.
1.3 Identify key players for security incident management
Incident response should follow a standard process, but each incident will have its own escalation process or call tree that identifies key participants.
Security Incident Response Team (SIRT)
Members may include:
Chief information security officer
Senior management
Security team staff
Help desk
Information owner
Information systems staff
Building and/or facilities management staff
Public affairs
Legal/compliance
Internal audit/risk management
Contractors
Horizontal Escalation
Engage additional resources, not senior-level management, when:
Analysts might not have the skillsets required to resolve an incident.
The escalation time frame has been exceeded.
Vertical Escalation
Engage senior-level management when:
An incident is beyond the scope and skillset of most staff.
Resources are not available to escalate horizontally.
There is a break in the horizontal escalation path.
More authority is needed for key decisions.
Vendor Escalation
Don’t forget to leverage vendors, but don’t depend on them.
Identify how vendors fit into your IT support structure and build them into your organization’s escalation path.
Engage vendors with issues that require specialized or deep skills/expertise.
Ensure that vendors provide a detailed report of their investigation of an issue.
Don’t overuse vendor contracts. Whenever possible, use in-house expertise to investigate and solve service problems.
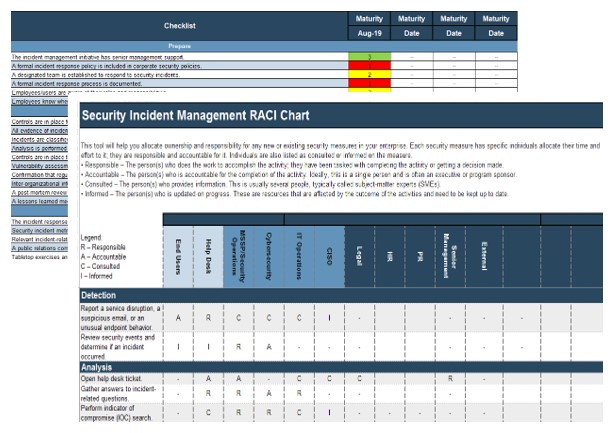
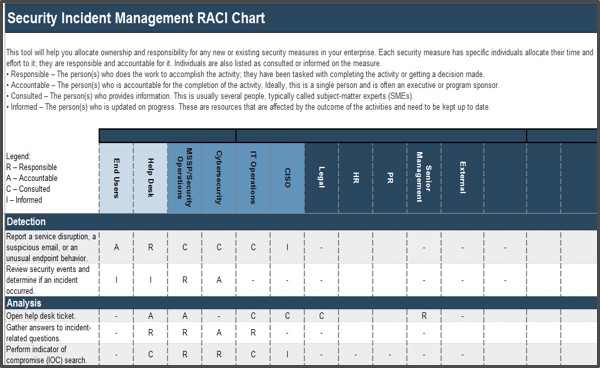
Assign responsibilities for the incident management process (RACI)
Complete the Security Incident Management RACI Tool and document your results.
Customize the header fields with applicable stakeholders.
Identify the stakeholders who are:
Responsible: The people who do the work to accomplish the activity; they have been tasked with completing the activity and/or getting a decision made.
Accountable: The person who is accountable for the completion of the activity; ideally, this is a single person and is often an executive or program sponsor.
Consulted: The people who provide information; there are usually several people, typically called subject matter experts (SMEs).
Informed: The people who are updated on progress; these people are resources and are affected by the outcome of the activities, so need to be kept up to date.